Security & DFIR
DFIR Windows 11 Volatile Memory Forensics & Volatility 3 Analysis
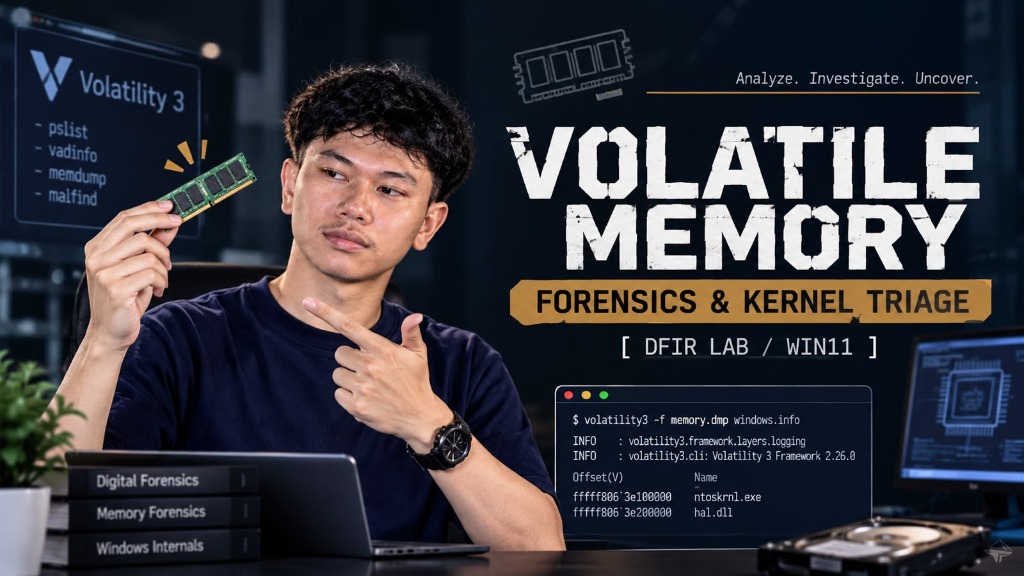
Live volatile RAM acquisition and deep kernel memory analysis on a Windows 11 host system to detect unlinked processes, inspect handles, and carve active memory artifacts.
System Implementation & Approach
Acquired 10 GB physical RAM via FTK Imager v8.3 with ring-0 kernel driver isolation. Conducted Volatility 3 analysis via dynamic Microsoft PDB symbol resolution (Build 26100), DKOM unlinked process detection via psscan, VAD PAGE_EXECUTE_READWRITE scanning via malfind, and in-memory DOCX carving via dumpfiles.
Role & Contribution
Individual forensic examiner: captured physical RAM dump, configured Volatility 3 Python framework, analyzed Windows 11 kernel paging structures, recovered terminated processes, and verified in-memory carved files.
Key Implementation Highlights
- Captured live physical RAM non-destructively to Drive D without pagefile contamination.
- Resolved Windows 11 Build 26100 kernel base (0xf803b8600000) and DTB (0x1ae000) via dynamic symbol tables.
- Carved in-memory file objects directly from physical offset 0xca8ea9f85350 with validated ZIP magic bytes.
Verification & Outcomes
- 10.72 GB raw physical RAM capture verified intact on disk (memdump.mem).
- Successful in-memory file carving of Tugas_06.docx with valid PK header bytes.
- Identified unlinked terminated processes and verified FTK Imager kernel driver handles.
Field Artifacts
Visual Evidence & Technical Artifacts
Sanitized assembly photos, live telemetry captures, and engineering verification artifacts.
Live 10 GB physical RAM acquisition using FTK Imager 8.3 without pagefile
Volatility 3 windows.info resolving Windows 11 Build 26100 kernel base and DTB
Pool carving via windows.psscan recovering terminated and unlinked processes with ExitTime
Audit of FTK Imager open handles to ad_driver.10.sys and target memory image
In-memory carving of Tugas_06.docx via windows.dumpfiles verified by PK magic bytes
Threat hunting via windows.malfind inspecting PAGE_EXECUTE_READWRITE VAD permissions and int3 traps