Security & DFIR
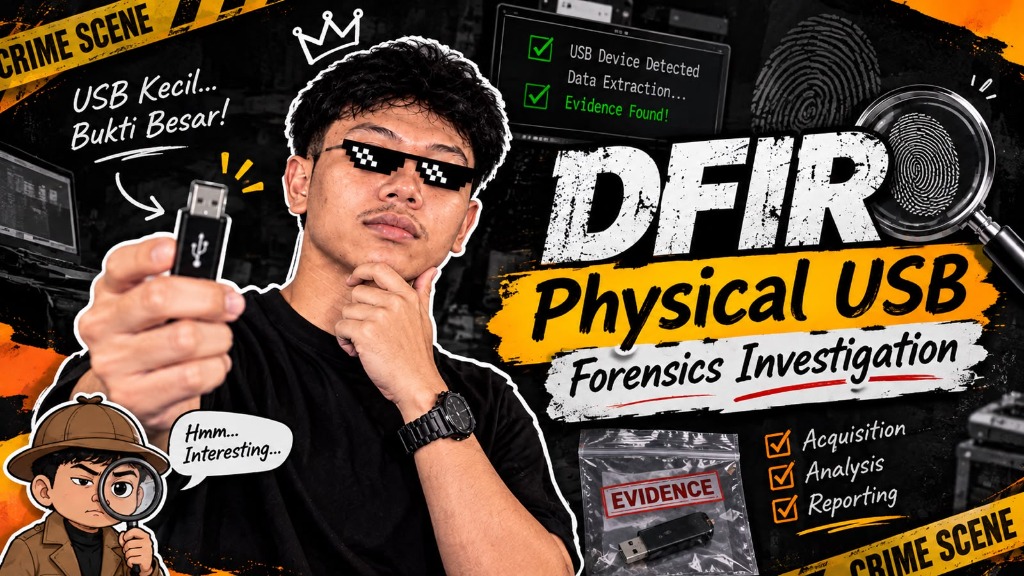
DFIR Physical USB Forensics Investigation
Digital forensic investigation recovering permanently deleted files and hidden evidence from a physical USB drive without altering the original device.
System Implementation & Approach
End-to-end digital forensics report (Case KASUS-USB-01) covering bit-stream imaging via FTK Imager, MD5 and SHA-1 integrity verification, MBR/exFAT partition analysis, and file carving in Autopsy.
Role & Contribution
Individual examiner: performed raw disk acquisition, verified cryptographic hash chains, carved deleted artifacts in Autopsy and HxD, and authored the formal forensic examination report.
Key Implementation Highlights
- Captured non-destructive raw bit-stream disk images to keep the original USB evidence forensically intact.
- Validated acquisition integrity before and after analysis using matching MD5 and SHA-1 cryptographic digests.
- Inspected MBR/exFAT allocation structures in HxD and recovered deleted file signatures with Autopsy.
Verification & Outcomes
- Zero hash mismatch between physical drive acquisition and working forensic image.
- Completed Case KASUS-USB-01 technical examination dossier archived on GitHub.
Field Artifacts
Visual Evidence & Technical Artifacts
Sanitized assembly photos, live telemetry captures, and engineering verification artifacts.
Cryptographic MD5 and SHA-1 dual-hash verification in FTK Imager confirming 100% bit-stream match with zero bad blocks
Autopsy file system tree parsing exFAT partition volumes, identifying active files, deleted records, and CLSID folder camouflage
Automated carving and keyword hit analysis recovering deleted credential file DATA PRIVASI RAHASIA.txt from unallocated space
HxD hex inspection revealing PK (50 4B 03 04) zip signature inside foto_kegiatan.jpg, exposing hidden embedded document archive