Security & DFIR
Ethical Penetration Testing Lab & Security Assessment Suite
Structured security testing manual and toolset for finding network weaknesses, protecting online privacy, and auditing Wi-Fi security ethically with four published audit reports.
System Implementation & Approach
Kali Linux and Windows 11 security lab organized by PTES and Cyber Kill Chain phases: OSINT DNS footprinting, Tor and Proxychains OPSEC hardening, full 65535 TCP/UDP Nmap scanning, Hydra brute-force error analysis, and WPA2-PSK 4-way handshake auditing with four published technical reports.
Role & Contribution
Individual author: documented 30+ step-by-step OPSEC verification proofs, conducted subdomain reconnaissance, executed full port audits and brute-force simulations, and authored four comprehensive penetration testing reports.
Key Implementation Highlights
- Organized isolated lab assessments strictly along PTES stages inside authorized local test environments.
- Validated traffic anonymization routes with Tor, Snowflake, and Proxychains verification checks before reconnaissance runs.
- Conducted full 65535 port scans to expose blindspots of standard top-1000 scans on exposed database services.
- Simulated Hydra brute-force credential attacks to verify MySQL host-based access control behavior.
- Authored four comprehensive audit reports in PDF format covering OSINT, OPSEC, scanning, and wireless pentesting.
Verification & Outcomes
- 30+ reproducible OPSEC verification proofs recorded with 100% Tor bootstrap and DNS leak prevention.
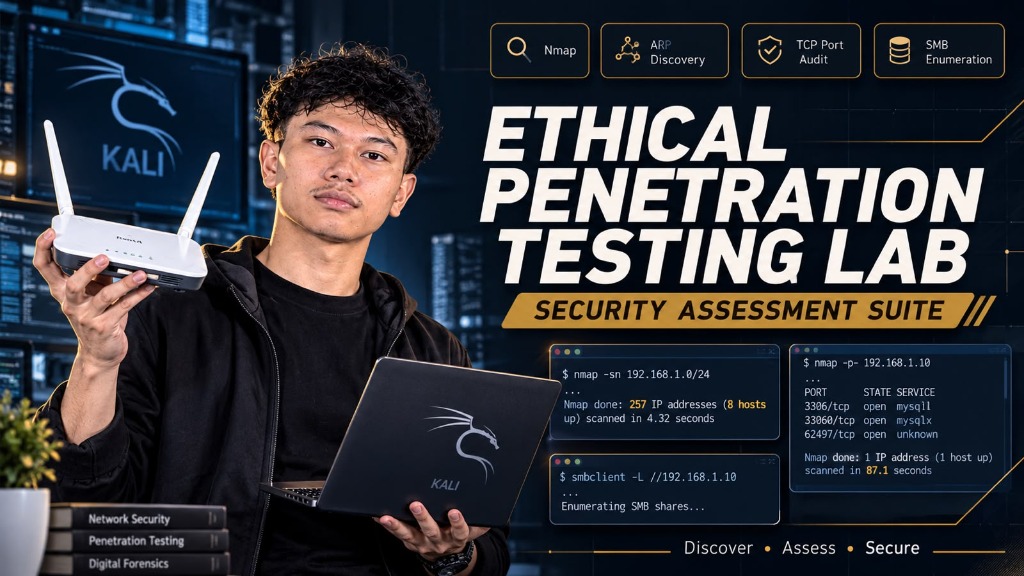
- 65535 TCP ports scanned in 87.1s, identifying 3 open ports (3306, 33060, 62497) and 65532 filtered ports.
- Verified SMB port 445 filtered by host firewall, preventing lateral movement exploits like EternalBlue.
- Hydra attack captured MySQL Error 1130 (Host is not allowed to connect), proving effective host isolation.
- Captured full WPA2 4-way handshake via deauthentication frame injection and verified PSK password recovery.
- All four modular audit reports compiled to PDF and archived in the official repository.
Field Artifacts
Visual Evidence & Technical Artifacts
Sanitized assembly photos, live telemetry captures, and engineering verification artifacts.
Layer 2 ARP sweep capturing 257 packets across 8 active subnet hosts without firewall interference
Full 65535 TCP port scan revealing ports 3306, 33060, and high port 62497 in 87.1 seconds
Service banner grabbing showing unauthorized MySQL status and 92% Windows 11 OS fingerprint match
SMB port 445 filtered verification confirming host firewall protection against lateral movement
Hydra credential brute-force simulation halted by MySQL Error 1130 host access control
Anonsurf iptables transparent proxy routing system traffic through Tor exit nodes
BrowserLeaks validation confirming Netherlands Tor exit IP and zero DNS leak leakage